
今回やりたいこと
前回の構成にL3SWを追加します。
また、今後拠点が増えることを考慮し、IPアドレスの設計を見直しました。
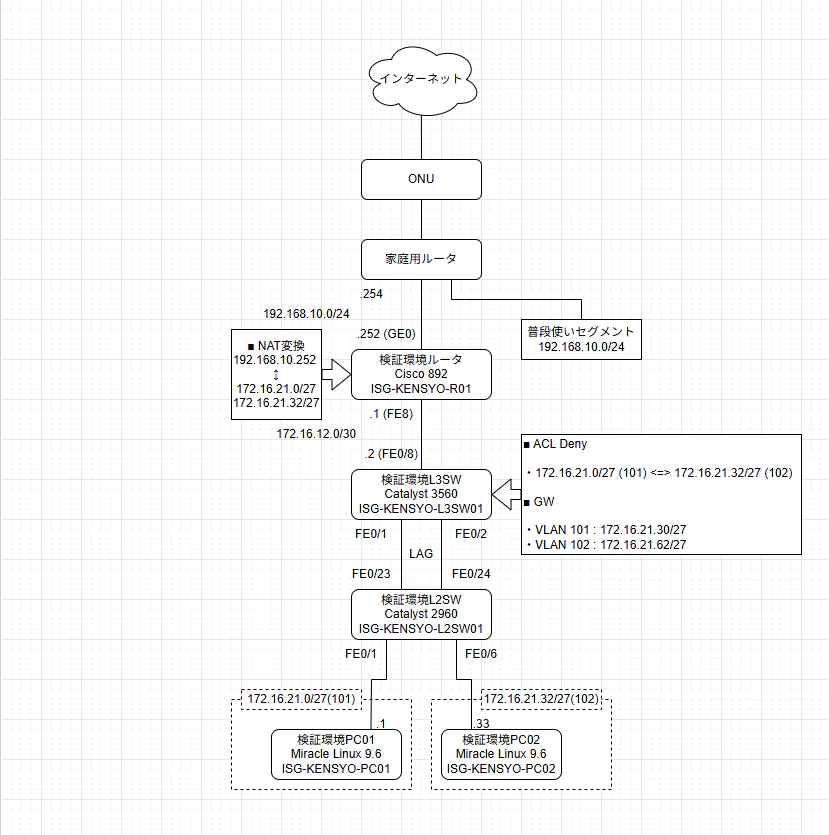
VLAN設計
VLANは以下の通り割り当てます。
| VLAN | 使用用途 |
|---|---|
| 1 - 100 | NW機器 |
| 101 - 200 | ユーザ利用 |
| 201 - 300 | サーバ IoT |
IPアドレス設計
172系のプライベートIPアドレスの割り当て
検証環境全体で、172系のプライベートIPアドレスを使用します。
今後拠点が増えることを考慮して、ナチュラルマスクの/16で分けて1拠点ごとに割り振ることにします。
| IPアドレス | 使用用途 |
|---|---|
| 172.16.0.0/16 | 今回の検証環境用(本拠地用) |
| 172.17.0.0/16 - 172.31.0.0/16 | 今後の拡張用(他拠点用) |
172.16.0.0/16内の割り当て
今回使用するプライベートIPアドレスです。これを/24で以下の通りサブネット化して使用します。
| IPアドレス | 使用用途 |
|---|---|
| 172.16.0.0/24 ~ 172.16.10.0/24 | 拡張用 |
| 172.16.11.0/24 ~ 172.16.20.0/24 | NW機器等 |
| 172.16.21.0/24 ~ 172.16.30.0/24 | ユーザ利用 |
| 172.16.31.0/24 ~ 172.16.40.0/24 | サーバ IoT |
| 172.16.41.0/24 ~ 172.16.255.0/24 | 拡張用 |
- 172.16.11.0/24 (機器管理用)
ここは機器管理用に予約しておきます。
-
172.16.12.0/24 (L3機器間用)
-
172.16.12.0/30
IPアドレス 使用用途 172.16.12.1 ISG-KENSYO-R01 FE8 172.16.12.2 ISG-KENSYO-L3SW01 FE0/8 -
172.16.12.4/30 ~ 172.16.12.252/30 (未使用)
-
-
172.16.21.0/24 (ユーザ利用)
-
172.16.21.0/27 (VLAN 101)
IPアドレス 使用用途 172.16.21.1 PC01 172.16.21.2 ~ 172.16.21.29 未使用 172.16.21.30 GW (Vlan Interface 101) -
172.16.21.32/27 (VLAN 102)
IPアドレス 使用用途 172.16.21.33 PC02 172.16.21.34 ~ 172.16.21.61 未使用 172.16.21.62 GW (Vlan Interface 102) -
172.16.21.64/27 ~ 172.16.21.224/27 (未使用)
-
- 192.168.10.0/24 (普段使いセグメント)
検証環境外の普段使いセグメントです。
172系をNAT変換するIPアドレスだけ確保しておきます。
| IPアドレス | 使用用途 |
|---|---|
| 192.168.10.1 ~ 192.168.10.100 | 固定 |
| 192.168.10.101 ~ 192.168.10.200 | DHCP |
| 192.168.10.201 ~ 192.168.10.250 | 検証環境間でのstatic NAT変換用 |
| 192.168.10.251 | 検証環境間でのDynamic Nat変換用(NAPT) |
| 192.168.10.252 | ISG-KENSYO-R01 |
| 192.168.10.253 | 予備 |
| 192.168.10.254 | 家庭用ルータ |
ポート収容
各機器のポート収容です。TorAは「Trunk or Access」です。
ISG-KENSYO-R01 (Cisco 892)
| Interface | TorA | 速度 | duplex | NWセグメント | 接続先 |
|---|---|---|---|---|---|
| FE 1 ~ 7 | - | - | - | - | 未使用 |
| FE 8 | - | auto | auto | 172.16.12.0/30 | ISG-KENSYO-L3SW01 |
| GE 0 | - | auto | auto | 192.168.10.0/24 | 家庭用ルータ |
ISG-KENSYO-L3SW01 (Catalyst 3560)
| Interface | TorA | 速度 | duplex | NWセグメント | 接続先 |
|---|---|---|---|---|---|
| FE 0/1 ~ 0/2 (LAG) |
Trunk | auto | auto | 172.16.21.0/27 (101) 172.16.21.32/27 (102) |
ISG-KENSYO-L2SW01 |
| FE 0/3 ~ 0/7 | - | - | - | - | - |
| FE 0/8 | - | auto | auto | 172.16.12.0/30 | ISG-KENSYO-R01 |
ISG-KENSYO-L2SW01 (Catalyst 2960)
| Interface | TorA | 速度 | duplex | NWセグメント | 接続先 |
|---|---|---|---|---|---|
| FE 0/1 | Access | auto | auto | 172.16.21.0/27 (101) | PC01 |
| FE 0/2 ~ 0/5 | - | - | - | - | - |
| FE 0/6 | Access | auto | auto | 172.16.21.32/27 (102) | PC02 |
| FE 0/7 ~ 0/22 | - | - | - | - | - |
| FE 0/23 ~ 24 (LAG) |
Trunk | auto | auto | 172.16.21.0/27 (101) 172.16.21.32/27 (102) |
ISG-KENSYO-L3SW01 |
構築後running-configとPCの設定
構築後のshow run結果を以下に記載します。
また、PCの設定は実行コマンドを記載します。
ISG-KENSYO-R01 (Cisco 892)
ISG-KENSYO-R01#show run
Building configuration...

Current configuration : 1691 bytes
!
! Last configuration change at 10:46:37 UTC Wed Feb 6 2036
version 15.2
service timestamps debug datetime msec
service timestamps log datetime msec
no service password-encryption
!
hostname ISG-KENSYO-R01
!
boot-start-marker
boot-end-marker
!
!
!
no aaa new-model
!
!
ip cef
!
!
!
!


!
!
!
!
no ipv6 cef
!
!
!
!
!
multilink bundle-name authenticated
!
!
!
!
!
!
license udi pid CISCO892-K9 sn FGL182322S2
!
!
!
redundancy
!
!
!
!
!
!
!
!
!
!
!
!
!
!
interface BRI0
 no ip address
 encapsulation hdlc
 shutdown
 isdn termination multidrop
!
interface FastEthernet0
 no ip address
!
interface FastEthernet1
 no ip address
!
interface FastEthernet2
 no ip address
!
interface FastEthernet3
 no ip address
!
interface FastEthernet4
 no ip address
!
interface FastEthernet5
 no ip address
!
interface FastEthernet6
 no ip address
!
interface FastEthernet7
 no ip address
!
interface FastEthernet8
 ip address 172.16.12.1 255.255.255.252
 ip nat inside
 ip virtual-reassembly in
 duplex auto
 speed auto
!
interface GigabitEthernet0
 ip address 192.168.10.252 255.255.255.0
 ip nat outside
 ip virtual-reassembly in
 duplex auto
 speed auto
!
interface Vlan1
 no ip address
!
ip forward-protocol nd
no ip http server
no ip http secure-server
!
!
ip nat inside source list LABtoRegular interface GigabitEthernet0 overload
ip route 0.0.0.0 0.0.0.0 192.168.10.254
ip route 172.16.21.0 255.255.255.224 172.16.12.2
ip route 172.16.21.32 255.255.255.224 172.16.12.2
!
ip access-list standard LABtoRegular
 permit 172.16.21.0 0.0.0.31
 permit 172.16.21.32 0.0.0.31
!
!
!
!
control-plane
!
!
!
!
mgcp profile default
!
!
!
!
!
!
line con 0
line aux 0
line vty 0 4
 login
 transport input all
!
!
end

ISG-KENSYO-R01#
ISG-KENSYO-L3SW01 (Catalyst 3560)
ISG-KENSYO-L3SW01#show run
Building configuration...

Current configuration : 1772 bytes
!
version 12.2
no service pad
service timestamps debug datetime msec
service timestamps log datetime msec
no service password-encryption
!
hostname ISG-KENSYO-L3SW01
!
boot-start-marker
boot-end-marker
!
!
!
!
no aaa new-model
system mtu routing 1500
authentication mac-move permit
ip subnet-zero
ip routing
!
!
!
!
!
!
!
!
spanning-tree mode pvst
spanning-tree etherchannel guard misconfig
spanning-tree extend system-id
!
vlan internal allocation policy ascending
!
!
!
!
interface Port-channel1
 switchport trunk encapsulation dot1q
 switchport trunk allowed vlan 101,102
 switchport mode trunk
!
interface FastEthernet0/1
 switchport trunk encapsulation dot1q
 switchport trunk allowed vlan 101,102
 switchport mode trunk
 channel-group 1 mode active
!
interface FastEthernet0/2
 switchport trunk encapsulation dot1q
 switchport trunk allowed vlan 101,102
 switchport mode trunk
 channel-group 1 mode active
!
interface FastEthernet0/3
!
interface FastEthernet0/4
!
interface FastEthernet0/5
!
interface FastEthernet0/6
!
interface FastEthernet0/7
!
interface FastEthernet0/8
 no switchport
 ip address 172.16.12.2 255.255.255.252
!
interface GigabitEthernet0/1
!
interface Vlan1
 no ip address
 shutdown
!
interface Vlan101
 ip address 172.16.21.30 255.255.255.224
 ip access-group deny10to20 in
!
interface Vlan102
 ip address 172.16.21.62 255.255.255.224
 ip access-group deny20to10 in
!
ip classless
ip route 0.0.0.0 0.0.0.0 172.16.12.1
ip http server
ip http secure-server
!
!
ip access-list extended deny10to20
 deny   ip 172.16.21.0 0.0.0.31 172.16.21.32 0.0.0.31
 permit ip any any
ip access-list extended deny20to10
 deny   ip 172.16.21.32 0.0.0.31 172.16.21.0 0.0.0.31
 permit ip any any
!
ip sla enable reaction-alerts
!
!
!
line con 0
line vty 5 15
!
end

ISG-KENSYO-L3SW01#
ISG-KENSYO-L2SW01 (Catalyst 2960)
ISG-KENSYO-L2SW01#show run
Building configuration...

Current configuration : 1581 bytes
!
version 12.2
no service pad
service timestamps debug uptime
service timestamps log uptime
no service password-encryption
!
hostname ISG-KENSYO-L2SW01
!
!
no aaa new-model
system mtu routing 1500
ip subnet-zero
!
!
!
!
!
!
!
spanning-tree mode pvst
spanning-tree extend system-id
!
vlan internal allocation policy ascending
!
!
interface Port-channel1
 switchport trunk allowed vlan 101,102
 switchport mode trunk
!
interface FastEthernet0/1
 switchport access vlan 101
 switchport mode access
!
interface FastEthernet0/2
!
interface FastEthernet0/3
!
interface FastEthernet0/4
!
interface FastEthernet0/5
!
interface FastEthernet0/6
 switchport access vlan 102
 switchport mode access
!
interface FastEthernet0/7
!
interface FastEthernet0/8
!
interface FastEthernet0/9
!
interface FastEthernet0/10
!
interface FastEthernet0/11
!
interface FastEthernet0/12
!
interface FastEthernet0/13
!
interface FastEthernet0/14
!
interface FastEthernet0/15
!
interface FastEthernet0/16
!
interface FastEthernet0/17
!
interface FastEthernet0/18
!
interface FastEthernet0/19
!
interface FastEthernet0/20
!
interface FastEthernet0/21
!
interface FastEthernet0/22
!
interface FastEthernet0/23
 switchport trunk allowed vlan 101,102
 switchport mode trunk
 channel-group 1 mode active
!
interface FastEthernet0/24
 switchport trunk allowed vlan 101,102
 switchport mode trunk
 channel-group 1 mode active
!
interface GigabitEthernet0/1
!
interface GigabitEthernet0/2
!
interface Vlan1
 no ip address
 no ip route-cache
 shutdown
!
ip http server
!
control-plane
!
!
line con 0
line vty 5 15
!
end

ISG-KENSYO-L2SW01
PC01 (MiracleLinux 9.6)
nmcli connection modify <インターフェイス名> ipv4.address 172.16.21.1/27
nmcli connection modify <インターフェイス名> ipv4.gateway 172.16.21.30
nmcli connection modify <インターフェイス名> ipv4.method manual
nmcli connection modify <インターフェイス名> down
nmcli connection modify <インターフェイス名> up
PC02 (MiracleLinux 9.6)
nmcli connection modify <インターフェイス名> ipv4.address 172.16.21.33/27
nmcli connection modify <インターフェイス名> ipv4.gateway 172.16.21.62
nmcli connection modify <インターフェイス名> ipv4.method manual
nmcli connection modify <インターフェイス名> down
nmcli connection modify <インターフェイス名> up
テスト
- PC01から
ping 8.8.8.8が通ることを確認する - PC01から
ping 172.16.21.62が通らないことを確認する - PC02から
ping 8.8.8.8が通ることを確認する - PC02から
ping 172.16.21.1が通らないことを確認する
次回の予定
機器管理VLAN, IPの設定とntpサーバの構築